- Version
- 6.0.10601-personal
- Studio or maker
- Vector 35 Inc.
- Languages
- English
- Activation
- Included
- Runs on macOS
- macOS 10.15 or later
- Chip type
- Apple Silicon, Intel 64-bit
The MCP server in Binary Ninja 6.0 is the kind of feature that makes you stop and think about how you work. It lets external tools talk to the analysis engine directly, which is useful when you have scripts or other programs that need to query the disassembly or decompiled output without a full GUI session. That is the spirit of this platform: it gives you deep control, but it presents it in a way that does not assume you have been doing reverse engineering for a decade.
What Binary Ninja is for
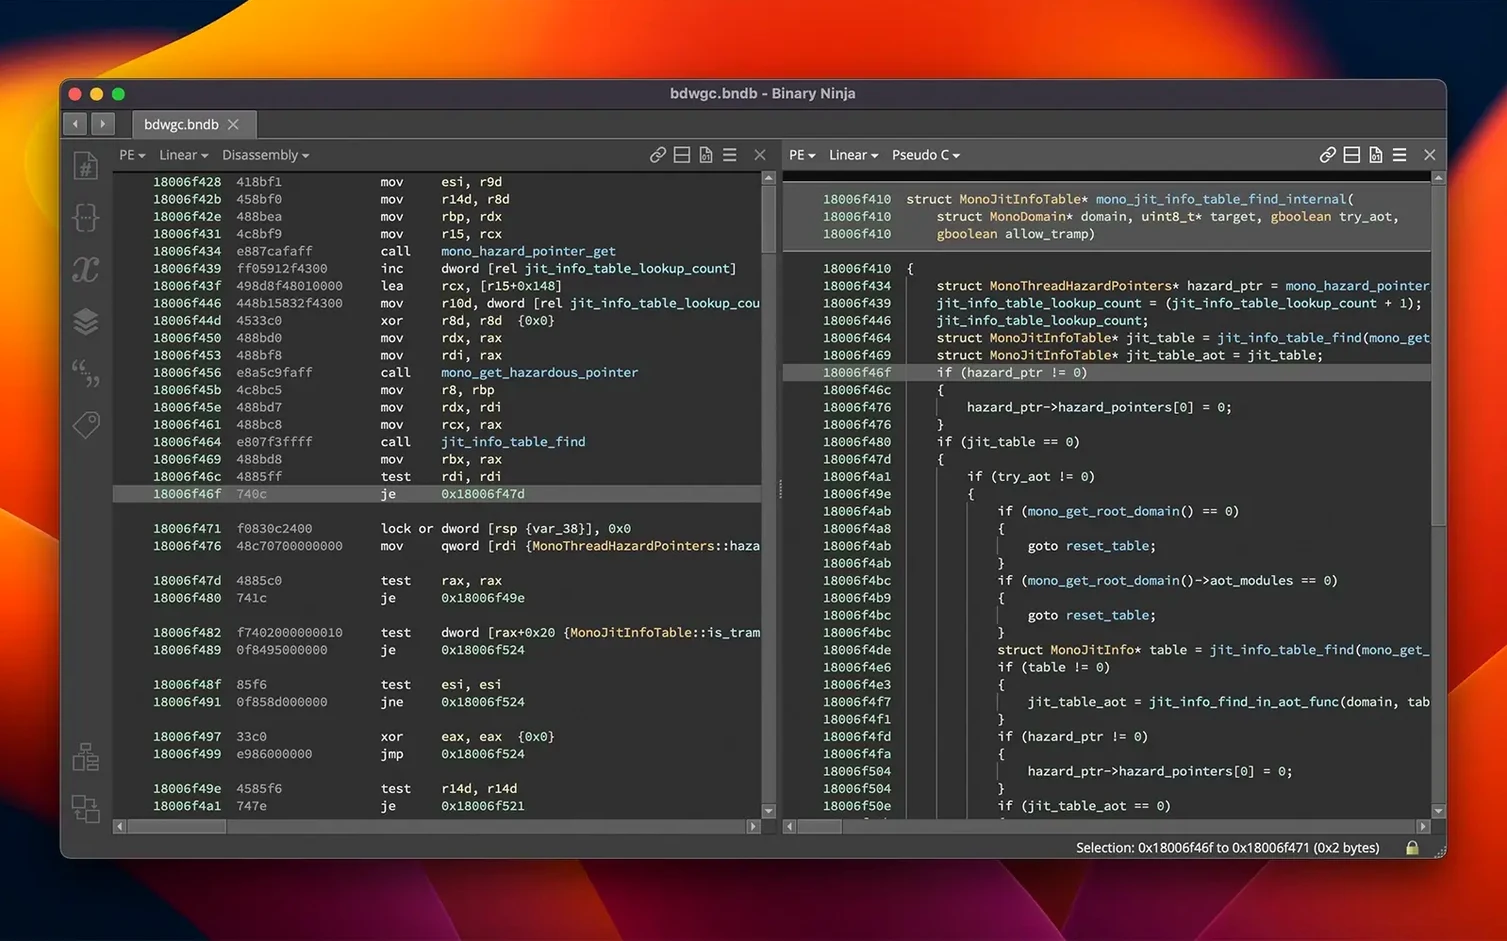
At its core, Binary Ninja is a reverse-engineering platform. It disassembles binaries, decompiles them into readable C-like pseudocode, and lets you analyze control flow and cross-references visually. You can patch binaries by editing assembly, applying preset patches, changing raw bytes in a hex editor, or even compiling C with the built-in SCC compiler. It supports common formats like PE, Mach-O, and ELF, and on macOS it handles ARM and x86 64-bit. If you are a security researcher, a malware analyst, or a curious developer who wants to understand how a program works, this is a tool that meets you where you are.
Who will get the most from it
Binary Ninja is not just for full-time reverse engineers. The batch processing and entropy graph help you find areas of interest in larger files quickly, and the API for C++, Python, and Rust means you can automate tasks or build your own analysis tools. It runs on Windows, macOS, and Linux, so it fits into mixed environments. For teachers like me, it is also a practical way to show students how assembly maps to source-level logic without overwhelming them. The interface is English, and it requires macOS 10.15 or later.
connect binary ninja to your debugger or fuzzer via the mcp server
Binary Ninja does not need to live in isolation. The new MCP server in version 6.0 means you can connect it to a debugger, a fuzzer, or a custom analysis pipeline without writing glue code that only works for one session. On macOS, it integrates naturally with the terminal and scripting workflows you already have. If you keep a few Python scripts in your home directory for parsing log files or extracting strings, you can point them at Binary Ninja's API instead of reinventing disassembly logic. The headless mode is especially useful here: you can run batch analysis overnight, then come back to a fully annotated binary the next morning.
For people working with multiple architecture types, the platform saves time by letting you switch between x86, ARM, PowerPC, or Z80 in the same project. You do not need a separate tool for each format. And since it supports PE, Mach-O, and ELF, you can analyze a Windows driver, a macOS framework, and a Linux shared library in one sitting without changing your workflow. If you are an analyst jumping between platforms, that consistency matters.
auto-analyze a suspicious Mach-O binary and see its control flow graph
Let me walk you through a session I set up for a colleague who was looking at a suspicious Mach-O binary. He opened the file in Binary Ninja and let the auto-analysis run. The control flow graph appeared immediately, showing function calls and basic blocks. He started by renaming a few key variables from generic names to something that matched the strings he saw in the data section. Then he applied types to the main data structures, which made the decompiled C output clearer.
He wanted to see how a particular function was called, so he used the cross-reference view to trace every caller. That led him to a loop that looked like it was decoding a buffer. He added a comment explaining the likely algorithm, then patched a conditional jump in the assembly to see what would happen if the loop ran differently. The built-in hex editor let him verify the byte changes before saving. The whole thing took maybe forty minutes, and he did not need to open a separate debugger or hex editor once. For a binary ninja torrent scenario where you want to work quickly, that is the kind of flow that keeps you in the zone.
A specific workflow: comparing two versions of a library
One task that comes up often is comparing two builds of the same library to find what changed. With Binary Ninja, I open the first version in one window and the second version in another. The Binary Similarity feature in 6.0 is designed for exactly this. I start by looking at the function list in both binaries, sorting by name to match them. Then I pick a function that looks suspicious and check its decompiled output side by side.
If the control flow graphs differ, I note the changed basic blocks and look for new or removed jumps. When I find a function that exists only in the newer version, I rename it based on its behavior and add a structure definition if it touches complex data. Finally, I export the annotated binary so the team can review it. The whole comparison uses the same platform, the same API if I want to automate it later, and no extra tools. For anyone doing binary ninja crack download research, that directness is the real value.
- Major release 6.0 added a new MCP server and a Binary Similarity feature.
- The Plugin Manager is now the Extension Manager, with a redesigned layout.
- Support for the TMS320C6x architecture was added.
- macOS 10.15 or later
- Intel or Apple Silicon
- English interface
Questions I keep getting
Can I patch a binary directly in Binary Ninja?
Yes, you can patch by editing assembly, using preset patches, changing raw bytes in a hex editor, or compiling C with the built-in SCC compiler.
How to install
- Open the package and follow the included install instructions to place Binary Ninja in your Applications folder.
- Read the activation notes in the package to get your copy running.
Similar apps
Sign in or join the club to leave a comment.
Nobody has commented yet.