- Version
- 6.5
- Studio or maker
- Objective Development
- Languages
- English, German
- Activation
- Included
- Runs on macOS
- macOS 14 or later
- Chip type
- Apple Silicon, Intel 64-bit
Every app on your Mac wants to talk to the internet, and most do so without asking. Little Snitch steps in when that happens, showing you a clear alert the moment an app tries to reach a server. You decide whether to allow it once, allow it always, or block it. Over time, you build a set of rules that matches how you actually work.
Requires macOS 14 or later and a clean install
Little Snitch 6.5 needs macOS 14 or later. It runs on both Intel and Apple Silicon Macs. The interface is available in English and German. Before you install, remove any previous version of Little Snitch — the new filtering engine replaces the older kernel-extension approach, so old parts can get in the way.
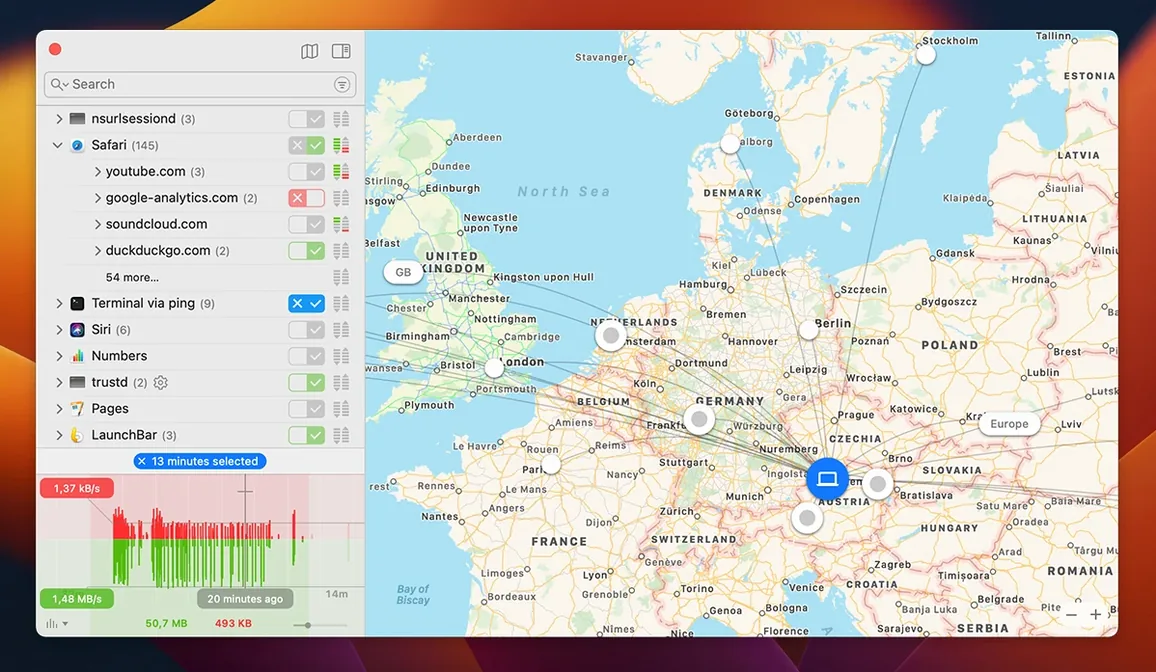
Main window lists apps, servers, a world map, and traffic history
The main window shows network activity as a list of apps and servers, a world map of connections, and an hourly traffic history. Alerts pop up when an app tries to make a connection, and the new engine watches app bundle integrity while the app is running — so a modified app gets noticed. The release notes mention a fix for a rare crash during exact-match process search, and expired temporary rules now show up under Suggestions > Expired. A command-line interface lets you configure settings and use scripts for automation.
Compatibility with macOS 27 Golden Gate is included, and encrypted DNS handling has been improved. There is also an experimental NAT64 implementation, which may interest you if you are testing IPv6-only networks.
Little Snitch 5.7 6 license key is a common search term, but the current version is 6.5 — and that is the one you want for a modern Mac running macOS 14 or newer.
This section covers what changed in daily use with recent updates, a complete workflow for a common task, typical beginner mistakes, and a few small conveniences hidden in plain sight.
Fewer false alerts with encrypted DNS
The jump to 6.5 is mostly about compatibility and behind-the-scenes reliability. If you use encrypted DNS, you will notice fewer false alerts — the improved handling means Little Snitch resolves names more consistently before showing you a connection request. For those who manage multiple Macs, the macOS 27 Golden Gate support means you can move to Apple's latest system without losing your firewall rules.
The experimental NAT64 implementation is worth knowing about if your network uses IPv6-only with a translation layer. It is marked experimental for a reason, but it means Little Snitch can handle connections that older versions would have silently dropped.
A small but welcome change: the label traffic amount is now traffic volume. This is not a feature, but it makes the Network Monitor easier to understand at a glance. The expired temporary rules fix under Suggestions > Expired saves you from hunting for rules you thought were gone.
App bundle integrity monitoring is the most visible new behavior. When an app is updated or modified while running, Little Snitch notices and may prompt you again — even for connections you already allowed. That is deliberate: it catches cases where a compromised update tries to use an old permission.
A complete workflow: create a rule set for a new app
Say you install a video editor that wants to phone home every few minutes. Here is how you build a clean rule set from scratch.
- Start with alerts on. Little Snitch will show a dialog for each connection attempt. Do not switch to Quiet Mode yet — you want to see what the app actually does.
- Allow connections that make sense. The app needs to check for license validation and download example footage. Allow those once or always, depending on your preference.
- Deny what does not belong. Analytics, crash reporters, and usage trackers get blocked. Use Deny in the alert dialog, and check Remember so you do not see that alert again.
- Review your rules. Open the main window and look at the rules list. You will see each allowed or denied destination grouped by app. Remove any rules you added by accident.
- Enable Quiet Mode after the first ten minutes. By now, most expected connections have been seen. Quiet Mode suppresses further alerts and lets the editor run without interruption.
- Check the Network Monitor after a few hours. The traffic volume column shows how much data went to each server. If an app you blocked is still sending packets, you will see it here — and you can investigate the discrepancy.
This approach works for any new app, from a web browser to a system utility. The key is to stay alert for the first few minutes, then let Quiet Mode take over.
Allowing everything the first day creates problems
Most new users run into the same few issues. Avoiding them saves time and frustration.
- Allowing everything the first day. When you see twenty alerts in a row, it is tempting to click Allow Always for every one. That creates a rule set that is too permissive and defeats the purpose. Instead, allow only connections you recognize and block the rest. You can always add a rule later.
- Forgetting to remove the old version. Little Snitch 6.5 uses a new filtering engine that does not play well with leftovers from version 5.x or earlier. If you skip the uninstall step, you may see duplicate alerts or no alerts at all.
- Using Quiet Mode from the start. Quiet Mode is useful after you have established rules, but using it immediately means you never see what your apps are doing. You end up with a blind spot that defeats the purpose of a firewall.
- Ignoring expired temporary rules. Temporary rules expire after a set time, but some beginners do not know where to find them again. Check Suggestions > Expired to see rules that lapsed — you can renew or delete them there.
- Not using the command-line interface for bulk tasks. If you manage multiple Macs, clicking through config screens on each one is slow. The command-line tool lets you export and import rule sets, saving hours of manual work.
Interactive world map shows unexpected server locations
Little Snitch includes features that do not appear in the main alerts but make daily use smoother.
- The interactive world map shows server locations visually. If you see a connection to a country you do not expect, it is a quick way to spot suspicious activity.
- App bundle integrity monitoring works silently in the background. You do not see it until an app changes — and then it saves you from trusting a modified binary with old permissions.
- Hourly traffic history is visible from the main window. This helps you notice when an app starts sending data at unusual times, like 3 AM for a word processor.
- The rules list includes a search field. If you have dozens of rules, searching for a specific app name or server is faster than scrolling. The exact-match search fix in 6.5 means this works correctly now.
People searching for little snitch 5.7 6 license key, little snitch mac crack, little snitch crack, little snitch torrent, or little snitch mac torrent are usually looking for older versions. Version 6.5 is the current release, and it runs on both Intel and Apple Silicon Macs under macOS 14 or later. The activation is included with your download, so there is no need to hunt for keys or cracks.
- Adds compatibility with macOS 27 Golden Gate.
- Monitors app bundle integrity while running.
- Adds an experimental NAT64 implementation.
- Improves encrypted DNS handling.
- macOS 14 or later
- Intel or Apple Silicon
- Interface languages: English, German
How to install
- Remove the previous version of Little Snitch before installing the new one — the old kernel extension can conflict with the new filtering engine.
- Follow the included installation and activation instructions to complete the setup.
Similar apps
Sign in or join the club to leave a comment.
Nobody has commented yet.